Agentic AI & AI Security Development
We design and build AI agents that automate real work, and the AI security that keeps them safe in production.
Creator of the ZeroHarmAI open-source security toolkit
What We Build
AI Agent Development
Custom AI agents and multi-agent workflows with RAG, MCP and tool integrations, memory, and evaluations, built for production.
AI Security Development
Guardrails, prompt-injection defenses, PII and secret redaction, red-team testing, and custom security tooling for LLM apps and agents.
Secure Agent Operations
Secure CI/CD, permissions, observability, monitoring, and governance so your agents stay reliable after launch.
Our Portfolio
ZeroHarmAI open-source tools for sensitive-data protection, agent security, and secure AI development workflows.
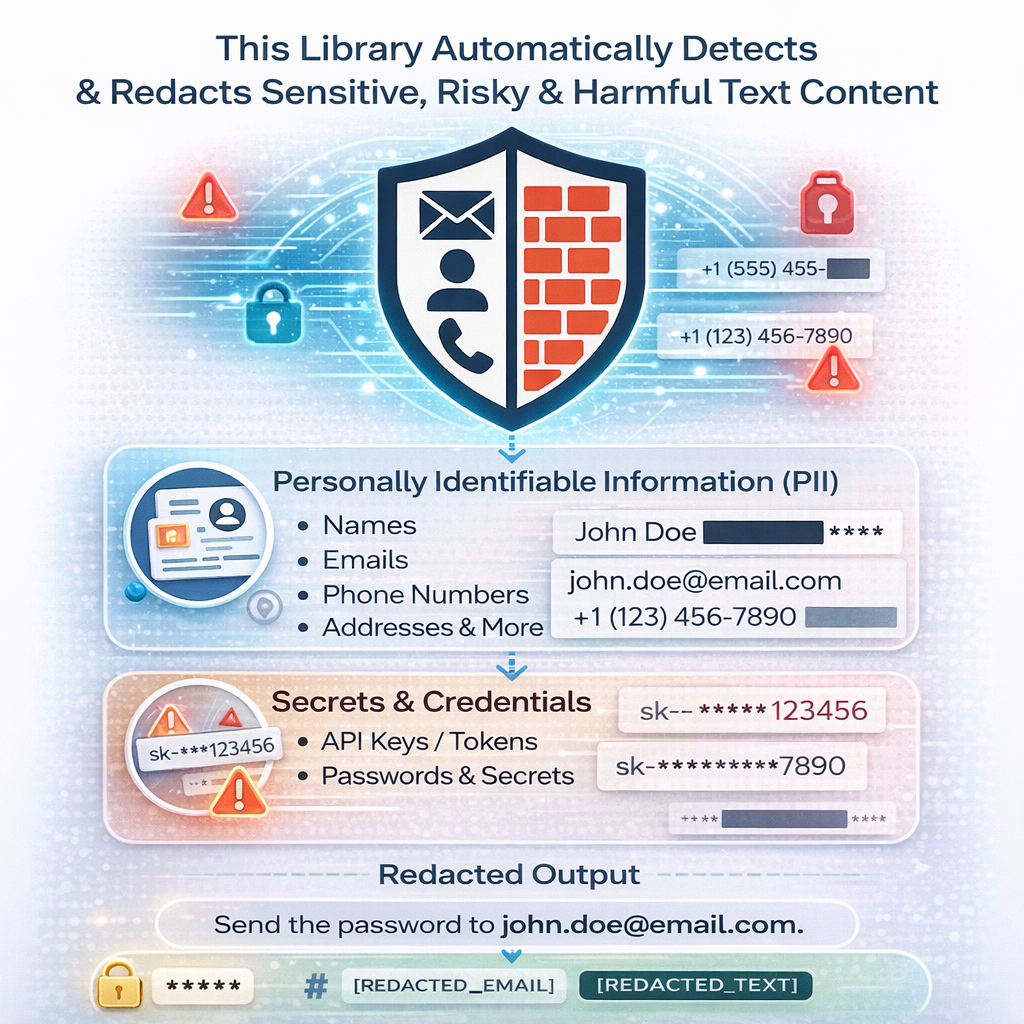
zero-harm-ai-detectors (Released)
AI Detectors is a Python-based AI safety and privacy protection library designed to automatically detect and redact sensitive, risky, and harmful content in text. It combines modern transformer-based AI models with high-performance heuristic detectors to balance accuracy, speed, and deployability.
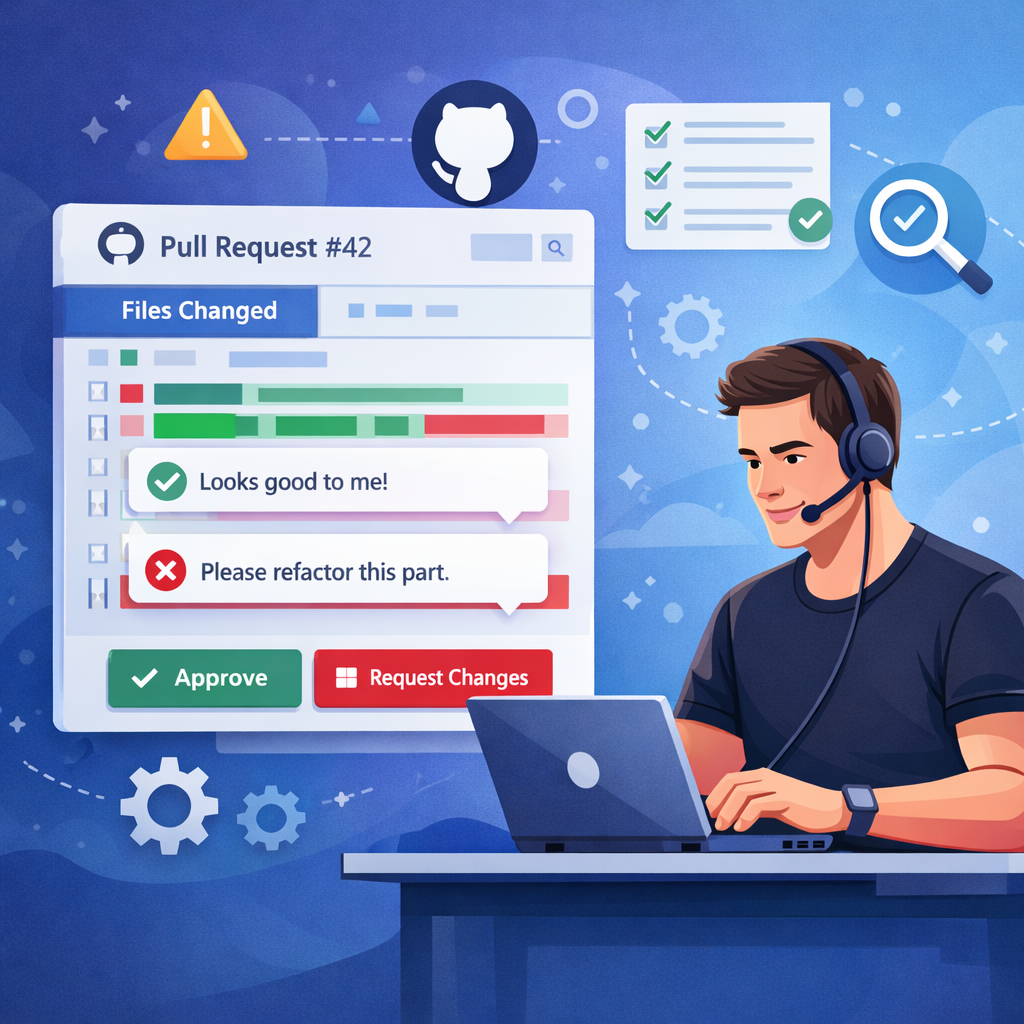
zero-harm-ai-gha (Released)
zero-harm-ai-gha is a GitHub Action for AI security reviews in pull requests. It scans code changes for prompt injection risk, PII and secret exposure, and unsafe LLM usage patterns before code is merged.
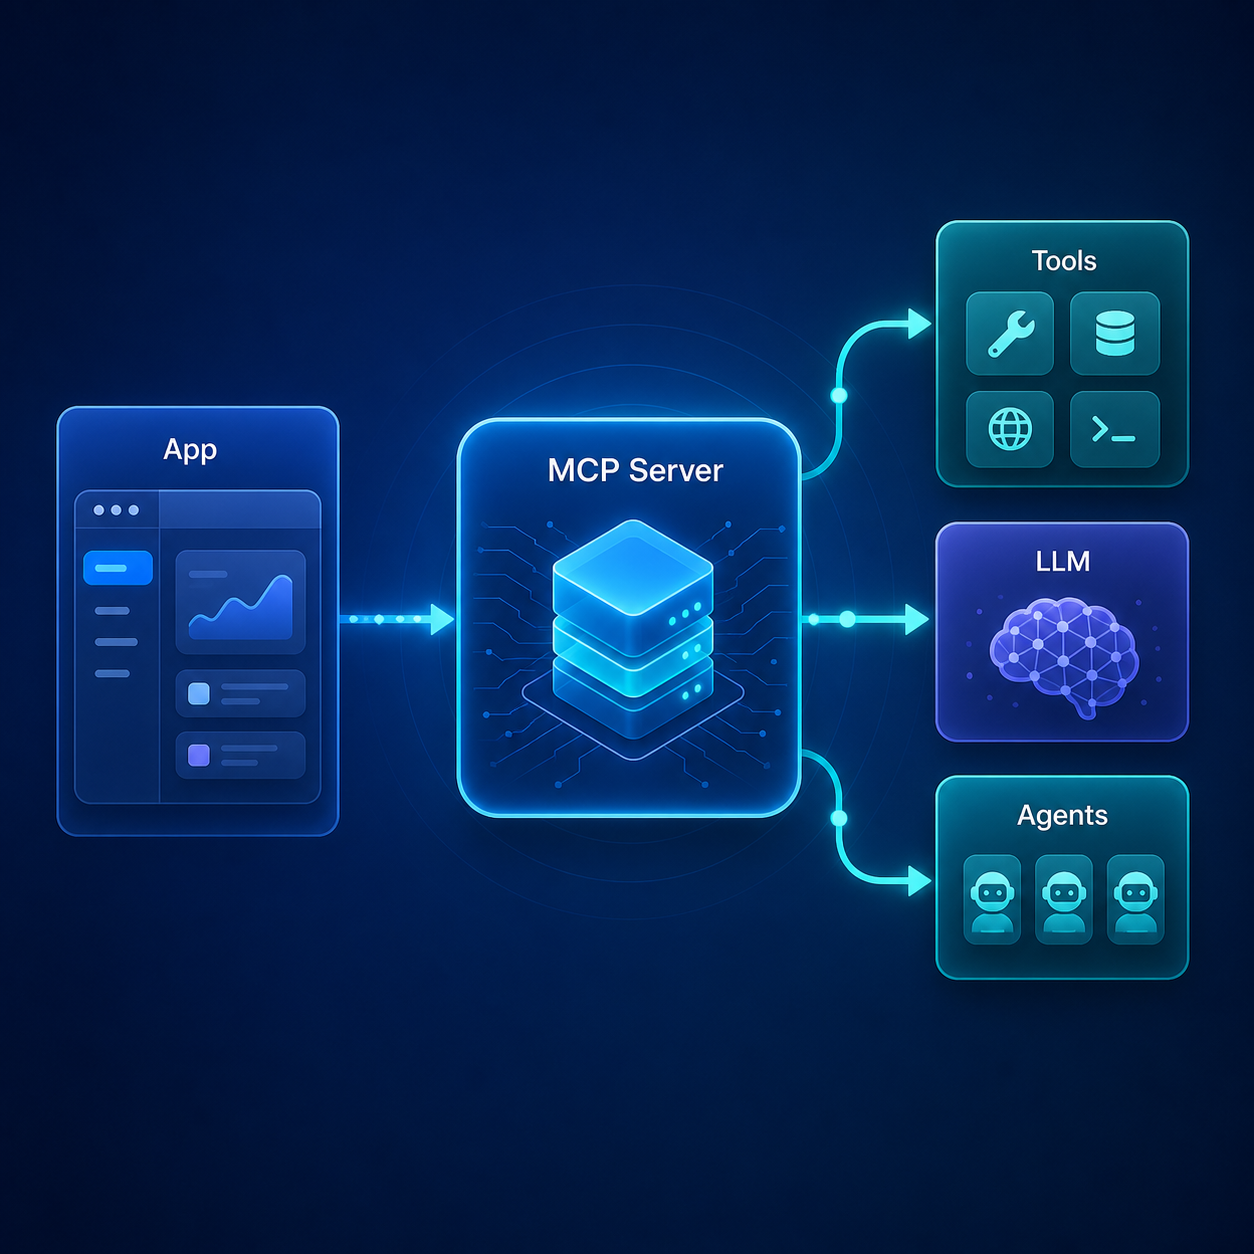
zero-harm-ai-mcp (Released)
zero-harm-ai-mcp is an MCP server for AI safety and privacy workflows. It gives applications and agents access to detection and redaction tooling for sensitive, risky, and harmful content.
Who We Work With
Startups
Build your first AI agents and AI-native products on a secure foundation.
Growing Companies
Turn agent prototypes into reliable, secured production systems that automate real work.
Enterprises
Agent development, AI security controls, and platform integration for complex environments.
Ready to Build AI Agents You Can Trust?
From first prototype to a secured production agent, we build it with you.